In the AI Agent Era, the Real Power May Sit With the OS Makers, Not the Model Labs
Apple is tightening Full Disk Access on macOS after the Meta Muse dispute. The bigger story is who controls access to files, mail, messages and payments.
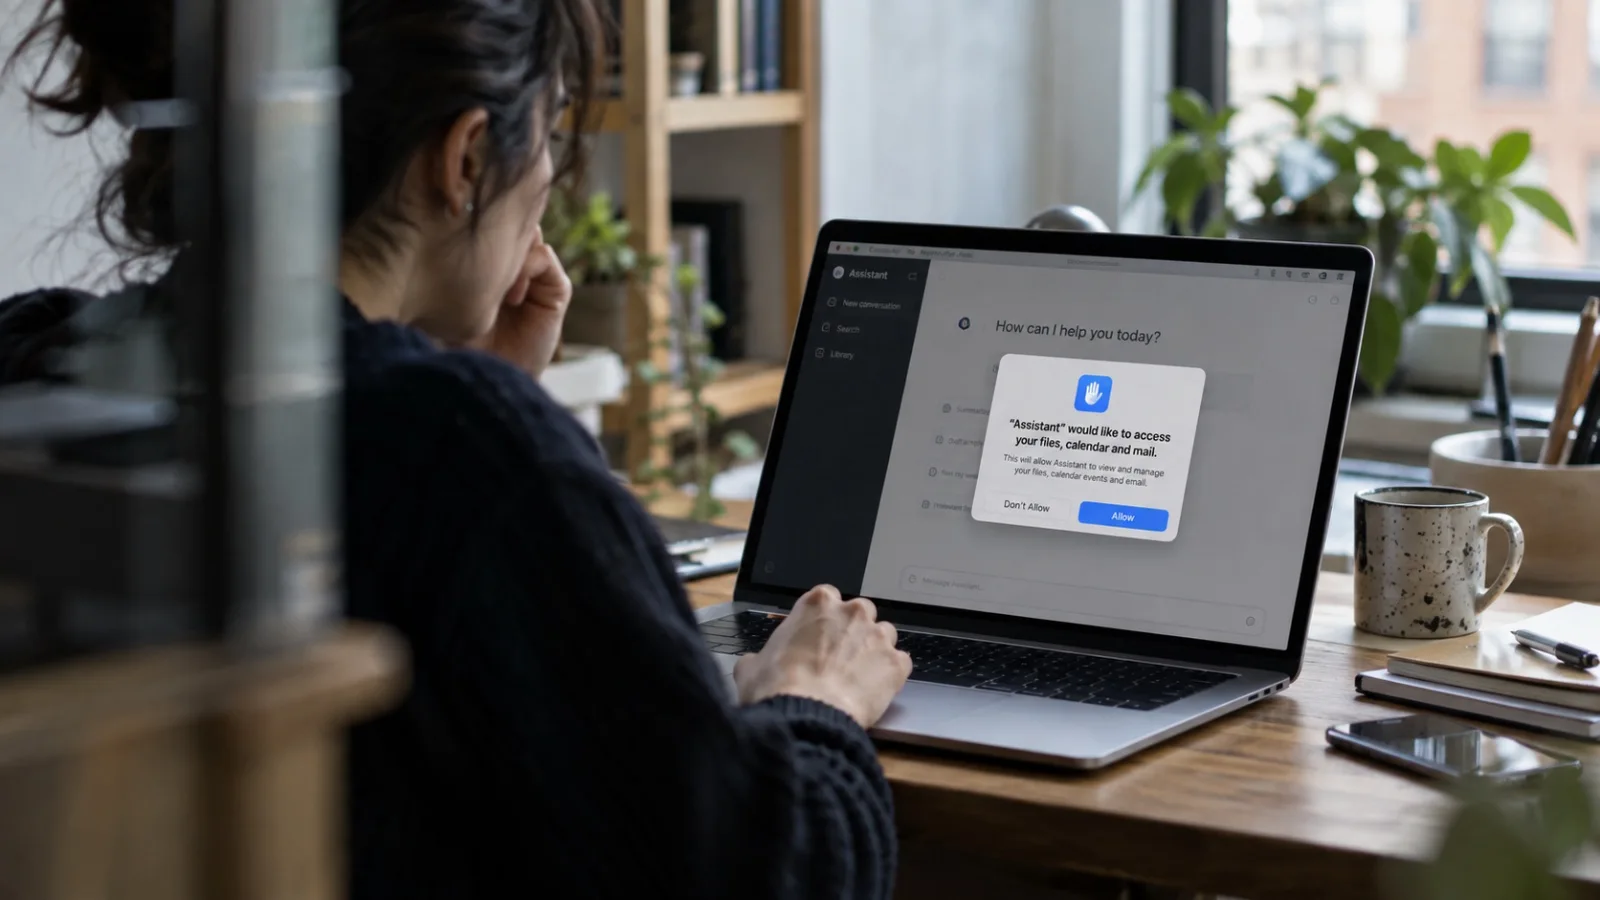
Apple said it will tighten control over Full Disk Access on macOS, just after the dispute over Meta's Muse. The news is not really about a security patch. It points to a larger issue: an AI agent's competitiveness depends not only on model intelligence, but on who controls its permission to reach files, email, messages and payments.
An agent's weakness is permission, not intelligence
A chatbot takes a question and answers it. An agent does more. To turn one sentence, "Get me ready for next week's business trip," into real work, it has to read the calendar, search email, operate the browser, open files, pay, book events and message colleagues.
That creates a new bottleneck for the AI industry. However smart the model, it cannot act without permission. Open every permission, and usefulness rises, but so do the risks: data leaks, malfunctions, prompt injection and excessive automatic execution.
Agent Utility ≈ Intelligence × Permission × Trust
The three factors work more like multiplication. If permission is zero, an intelligent agent's real ability to act is close to zero. If permission is broad but users do not trust the agent, consent is hard to get.
Why Apple's announcement matters
Apple said on Oct. 2 that it will add controls to Full Disk Access. The feature was built for programs that need access to all data on a Mac, such as cloud backup. Apple noted that some developers use it in ways that can expose files, Mail, Messages and browsing history without the user fully understanding.
One sentence stands out. Apple said that as AI agents grow more powerful and autonomous, the risk from this level of access will grow "significantly." It has not disclosed timing or the user experience. The direction is clear, though: on the Mac too, broad agent access will likely need stronger confirmation from the user.
The Muse dispute calls for care. A user claimed Muse read private Messages he had not allowed. Meta disputed that. By the company's account, Muse can read Messages content only if the user turns on both Full Disk Access and the Messages connector, and access can be revoked at any time. On the facts confirmed so far, it is hard to say Muse secretly read messages.
The OS becomes a gatekeeper again
In the mobile era, platform power came from the App Store. Apple decided which apps reached the iPhone, which APIs they could use and how payment rules applied.
The question in the agent era runs deeper. Which AI can read a user's email? Which can edit files? Which can pay? Which can give commands to outside systems on the user's behalf?
- Apple: Strong control over personal data and device permissions across macOS, iOS, Messages, Photos, Contacts, Calendar, Keychain and Apple Pay.
- Microsoft: Through Windows, Microsoft 365 and Entra identity, a position to run agent-specific accounts, least privilege, auditing and enterprise authorization.
- Google: Through Android, Chrome, Google accounts and Workspace, a link point for mobile actions, the browser, identity and personal context.
Microsoft and Google are moving the same way
This reading does not rest on Apple alone. For agent features in Windows, Microsoft is designing agent accounts separate from human accounts, limited permissions, isolated workspaces and explicit user approval. The agent starts with minimum privilege and reaches only the files and resources the user allows.
Google, describing agentic features in Android, names explicit user control, data protection and operational transparency as core principles. As Android shifts from a plain OS to an intelligence system that understands context and carries out tasks, the OS itself becomes the security layer that sets how far an agent can act.
That does not mean model companies are weaker
Concluding that "OS wins, model makers lose" would be premature. Companies such as OpenAI, Meta and Anthropic are strong in model performance, agent UX, cloud execution and connector ecosystems. Many agent tasks can run on cloud VMs and SaaS APIs alone.
But the deeper an agent reaches into a user's digital assets, such as local files, Messages, device context, passwords and payments, the more approval power shifts to the OS and identity providers. So power in the agent market is more likely to be redistributed among models, operating systems, browsers, identity and payments than held by any one company.
What changes for AI investors
| Earlier AI contest | Agent-era contest | What investors should watch |
|---|---|---|
| Model benchmarks | Real action success rates | Task completion rate after permission is granted |
| Token cost | ROI per task | How much human clicking and time is replaced |
| API ecosystem | Permission / identity ecosystem | Ties to the OS, Entra, Google Account and Apple account |
| Chat UX | Trust UX | How easy approval, logs, revocation and audit are |
Insight Times Editorial Desk